

NVIDIA OpenShell
Open, secure runtime for AI agents. It governs agent execution, access, and where inference goes.
The Secure Runtime for Autonomous Agents
Give agents the access they need to execute on the tasks you send them. NVIDIA OpenShell combines sandboxed execution, controlled resource access, credential protection, and formal policy verification, with enforcement outside the agent workload.
Manage agent behavior outside of its environment. OpenShell governs how agents interact with enterprise systems, data, and external services.
- Agent-native infrastructure: OpenShell separates agent logic from the interfaces that connect it to its environment and to external systems. Execution is instrumented, and every action passes through policy enforcement.
- Deployment flexibility: Run open or closed models with your choice of agent and harness across supported local, cloud, hybrid, on-premises, and air-gapped environments.
- Deterministic governance: Deny access by default and grant permissions scoped to the declared task. OpenShell enforces policy outside the agent process, where enforcement cannot be influenced by model output.
OpenShell is the secure runtime in the NVIDIA Open Agent Safety Platform, an open reference system design for full-stack agent control that combines OpenShell and NVIDIA Sentry with NVIDIA BlueField-4 in-silicon security enforcement.
The OpenShell Architecture
OpenShell combines individual sandboxes, runtime supervision, centralized management, and formal policy verification to govern agent execution.
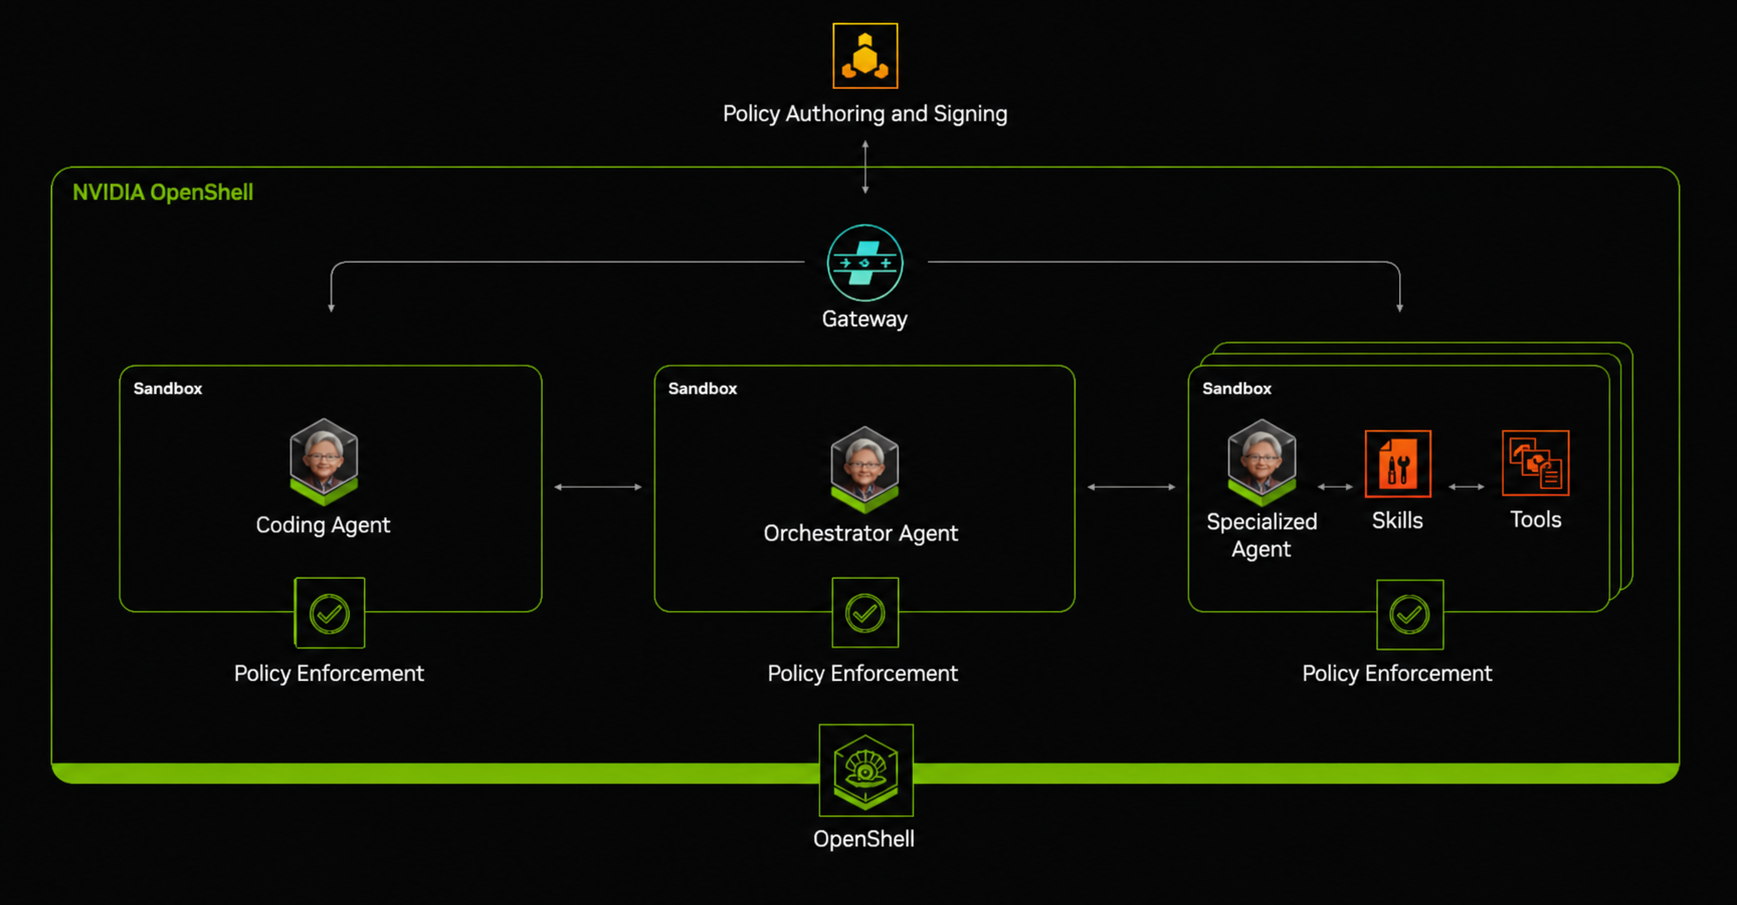
1. Agent Sandboxes
Isolate the workload and define its boundaries
Each sandbox runs an agent workload and has kernel-level controls over the file systems and networks the agent accesses. Those controls remain in place when the agent runs generated code or launches child processes. Network access passes through the supervisor for policy enforcement.
2. Supervisor
Enforce access policies outside the agent workload.
Each sandbox has a supervisor that checks outbound requests against policy. For configured HTTP, GraphQL, and Model Context Protocol (MCP) traffic, it can allow a read while blocking a write through the same API. The supervisor also keeps real service credentials outside the workload, substituting them only after network access and credential authorization checks pass.
3. Gateway
Manage sandbox lifecycles and policies across your fleet.
The OpenShell Gateway manages the lifecycles and policies of many sandboxes. Govern individual workloads and groups, with separate workspaces, permissions, and service access for teams sharing infrastructure.
4. Policy Prover
Verify the permissions a policy grants.
Use formal logic to check whether modeled permissions stay within operator-defined boundaries, including access contributed by service providers. The policy prover can establish that those permissions remain within a boundary or identify a concrete action that exceeds it, giving human and AI reviewers evidence to assess proposed policy changes.